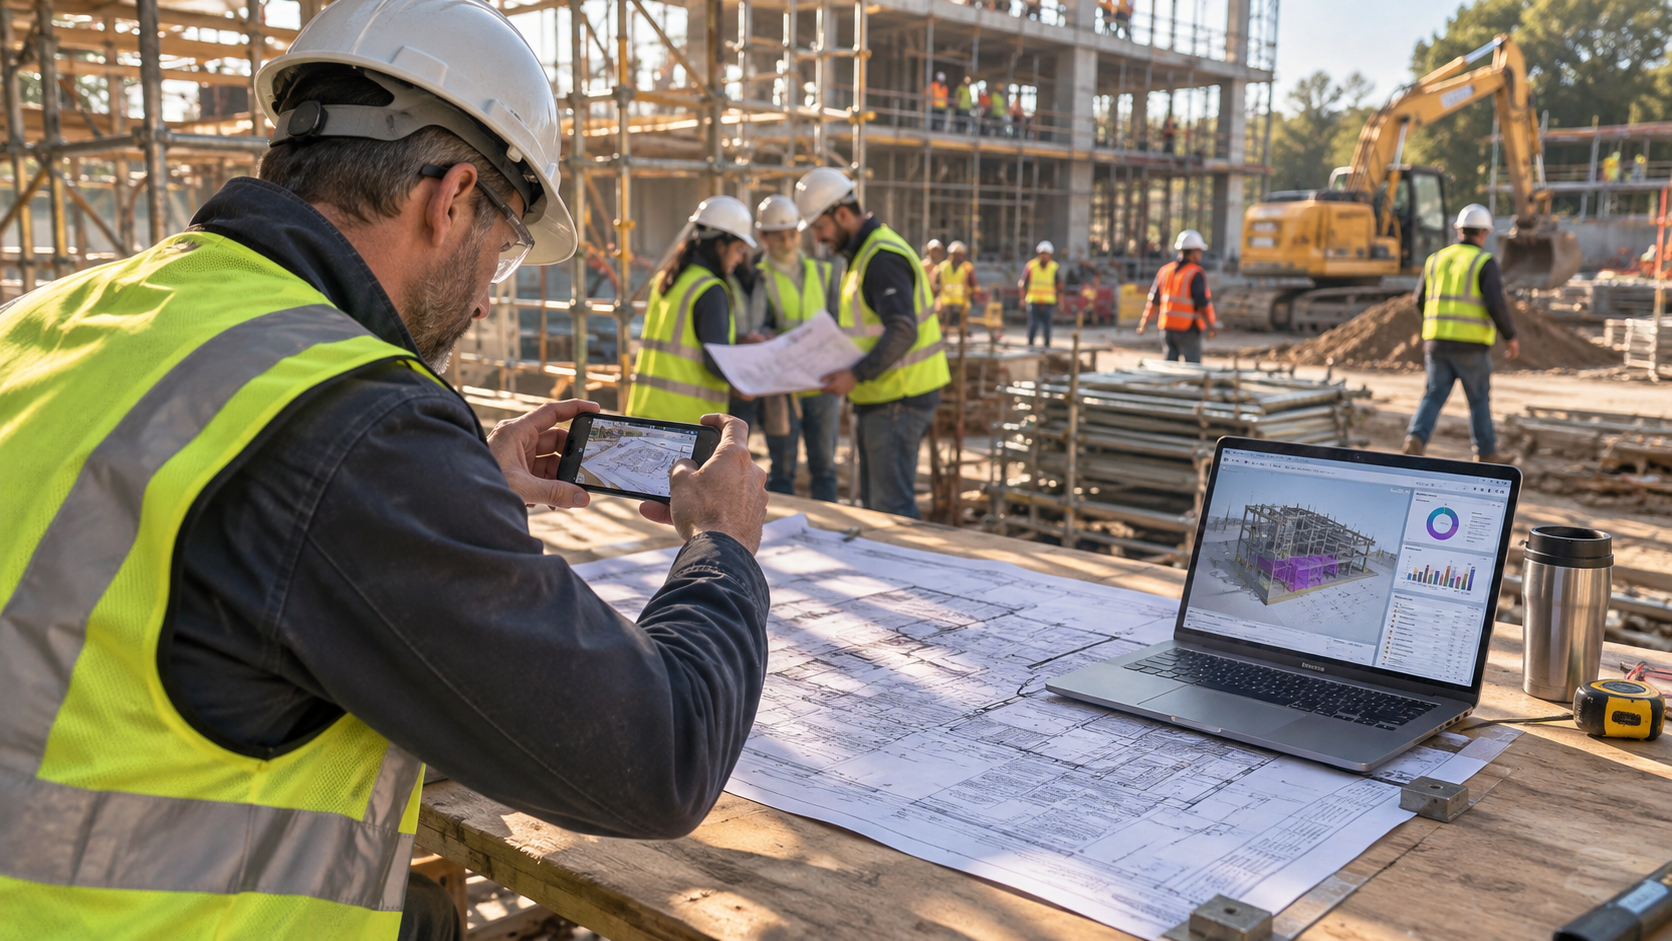
Illustrative scenario. A superintendent photographs drawings on a personal phone and uploads them to an AI tool for a quantity takeoff. The drawings may contain information the contract treats as controlled. The firm never approved the tool.
The superintendent has found a quicker way to do the job. Before that becomes routine, the firm needs to know where the drawings are being sent. The same question applies to schedule information and other project materials.
IBM’s 2025 Cost of a Data Breach Report studied 600 organizations that experienced breaches between March 2024 and February 2025. One in five of those organizations reported a breach linked to shadow AI, meaning AI used without employer approval or oversight. Organizations with high levels of shadow AI had average breach costs $670,000 higher than those with low levels or none. Among the breached organizations studied, 63% had no AI governance policy or were still developing one. IBM report findings
Contractors handling federal contract information (FCI) or controlled unclassified information (CUI) should include AI tools in their data-flow review and apply the CMMC requirements relevant to their work. A device list alone will not capture the services used on those devices. CMMC scoping
Three practical steps
- Find the tools already in use. Include personal AI accounts used for work, browser extensions, AI features in project and document software, and field applications that send images or text to external models. You cannot set a rule for a tool you cannot name.
- Write the rule on one page. Allow public information, published material, and generic process questions. Keep controlled drawings and specifications, bid strategy, owner information, and other nonpublic material out of unapproved tools. Make the rule usable on a job site.
- Teach the prompt and the photo. Show crews what to remove from prompts and job-site images before sharing them. Keep the training short, practical, and relevant to the work they do.
Connect AI and device inventories
CMMC Level 1 scoping concerns systems that process, store, or transmit federal contract information (FCI). Level 2 scoping uses defined asset categories, including assets that handle controlled unclassified information (CUI), assets that provide security protection, and contractor risk-managed assets. It is not limited to devices that directly hold CUI. Use the applicable scoping rules to classify AI tools and the systems they rely on. CMMC scoping requirements
Link the device, application, and vendor records so the project team can follow where information is sent.
Check the inventory as crews and project phases change. It should reflect the tools in use on the job, not just those recorded at notice-to-proceed.
Assign someone to review new tools and uploads as crews and project requirements change.